Rafay and Fortanix Bring Attested Confidential AI to Kubernetes Pods
Why the Pod Is the Right Place to Draw the Line
Rafay Systems and Fortanix have pushed confidential AI past the virtual machine and down to the Kubernetes pod, which is where most AI teams actually deploy. That's a meaningful move, and it's easy to underrate. Confidential computing has been around long enough that most infrastructure people can recite the pitch, but a VM-level boundary never fit neatly into how modern AI workloads get packaged and shipped. The pod is the unit teams actually think in, and that's the point (and this is the part most people overlook): protecting the pod means protecting the thing that gets scheduled, scaled and updated every day.
The announcement, made at KubeCon + CloudNativeCon North America 2026 in Sunnyvale, Calif., lets neoclouds, sovereign AI clouds and enterprises sell confidential AI as a managed service rather than a bespoke project. Here's the thing: the managed part is where most of the value sits for buyers. A bespoke confidential deployment might work once, but it rarely survives a second customer. Not a small distinction.
How the Pieces Fit Together
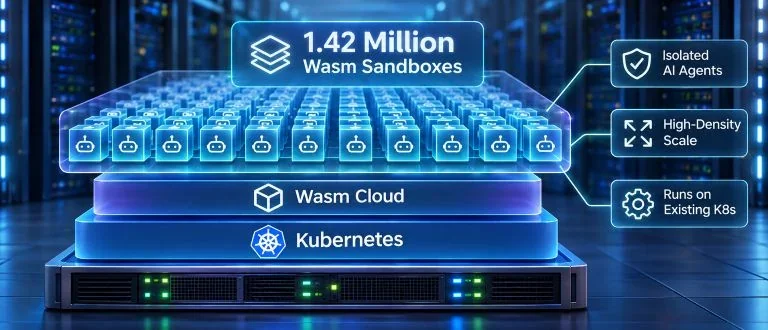
The plumbing sits on CNCF Confidential Containers (CoCo), an incubating project built on Kata Containers. Each pod runs in its own lightweight confidential virtual machine, and the CPU encrypts its memory. That's the detail that makes the pod-level claim credible, because isolation rests on hardware-backed memory encryption rather than on configuration alone. On supported hardware, GPUs fall inside the trust boundary too, which matters a lot for AI since the accelerator is usually the most expensive part of the stack.
Fortanix Confidential Computing Manager performs composite attestation across CPU and GPU trusted execution environments, plus firmware and software components. Fortanix Data Security Manager then releases encryption keys only to environments that pass. If attestation fails, the keys stay locked and the workload never touches sensitive data.
Attestation is only as good as the list of things it measures. Composite attestation covers more components than a single check would, which is the whole idea, but every added component is another thing that has to be enumerated correctly and kept current. Systems like this typically fail at the edges, such as a firmware version nobody tracked or a driver nobody pinned, rather than in the core cryptography. That's not a knock on the design. It's just where I'd look first.
Turning Confidential Clusters Into a Product
The harder problem for providers has been operations, not cryptography. Getting a confidential VM to boot is one thing. Keeping that setup consistent across many clusters, with different owners and different upgrade schedules, is another. Rafay handles that layer. Its blueprints install the Fortanix CoCo add-ons and keep them synchronized across every confidential cluster. Operators onboard GPU infrastructure once, then give each customer an isolated tenant.
From there, administrators package a confidential workload as a SKU in Rafay SKU Studio. End users launch it on demand from the Rafay Developer Hub without opening a support ticket. Policy, access controls and quotas apply across tenants and clusters, so the provider doesn't have to stitch those together by hand. That last part is easy to skip past, but it's where many managed platforms either earn their margin or give it away. A SKU turns a security architecture into something a sales team can price and a customer can order, which is a different thing from something an engineer can build.
“With Confidential Containers, that model now reaches the Kubernetes pod, where AI teams already ship their workloads,” said Mohan Atreya, chief product officer at Rafay. Anuj Jaiswal, chief product officer at Fortanix, said model owners, enterprises and operators each want assurance that the others cannot see what they own. “Fortanix Confidential AI releases keys only to attested workloads,” he said. Both statements are product-facing, and you should read them that way. The useful part is the framing: three parties with competing interests, one shared infrastructure, and a claim that none of them has to trust the others.
Availability and the Gap It Targets
Rafay support for CoCo-based deployments with Fortanix Confidential AI is available now, alongside the existing confidential VM integration. That means providers aren't being asked to migrate off a working setup to get the pod-level option. Fortanix first announced Confidential AI support for CoCo on Oct. 19, so this release builds on an earlier step rather than arriving cold. The two companies are extending a stack that's already in market, which makes it easier for a provider to pilot the new option without starting from scratch.
The timing reflects a verification problem. Research from Fortanix and Atomik Research found that 93% of AI leaders understand traditional encryption doesn't protect data while AI processes it. Only half can fully verify that protection is in place during inference. That gap, more than any single feature, is what this integration is built to close. I'd call that the real story here. Encryption at rest and in transit is well understood, but encryption during computation is still hard to prove to an auditor or a customer. And yet it's often treated as an assumption rather than something anyone checks.
What This Means Going Forward
Here's the thing: this is less a product launch than a signal about where confidential computing is headed. If the pod becomes the unit of protection, the security boundary moves to where developers already work, and that's usually what gets security adopted. Whether that holds depends on how many providers actually pick it up, and the source material doesn't say. I won't guess at adoption numbers or timelines.
What it does mean, if you're running AI on shared infrastructure, is that the question changes. Instead of asking whether your data is encrypted, you'll start asking whether you can see the attestation result and who controls the key release policy. That's a more useful set of questions, and most teams aren't asking them yet. The integration looks credible, and the operational story is its strongest part. The open question is whether verification becomes routine or stays a premium feature that only well-funded buyers can afford.